Watch
See CRYPTAGION in action.
An illustrative fixture walkthrough of discovery, CBOM, scoring and roadmap. Figures are hypothetical; see the verified Python case study below.

Discover cryptography across source code, certificates and TLS — inside your perimeter.
CRYPTAGION generates a CycloneDX 1.6 CBOM, prioritises classical and quantum risk, and turns the inventory into an actionable migration roadmap, with a board-ready PDF that supports your DORA, NIS2 and EU Cyber Resilience Act evidence.
Illustrative fixture metrics; no customer exposure or migration estimate inferred — inspect the verified Python case study.
CRYPTAGION supports compliance activities; use of the product does not by itself establish regulatory compliance.
An illustrative fixture walkthrough of discovery, CBOM, scoring and roadmap. Figures are hypothetical; see the verified Python case study below.
Three independent forces have made cryptographic inventory a 2025 board topic.
FIPS 203 (ML-KEM), FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA) shipped in August 2024. The "we're waiting for standards" excuse expired.
DORA, NIS2, and the EU Cyber Resilience Act increase the need for demonstrable ICT resilience, cryptographic governance, and audit-ready evidence — that your existing GRC tooling can ingest.
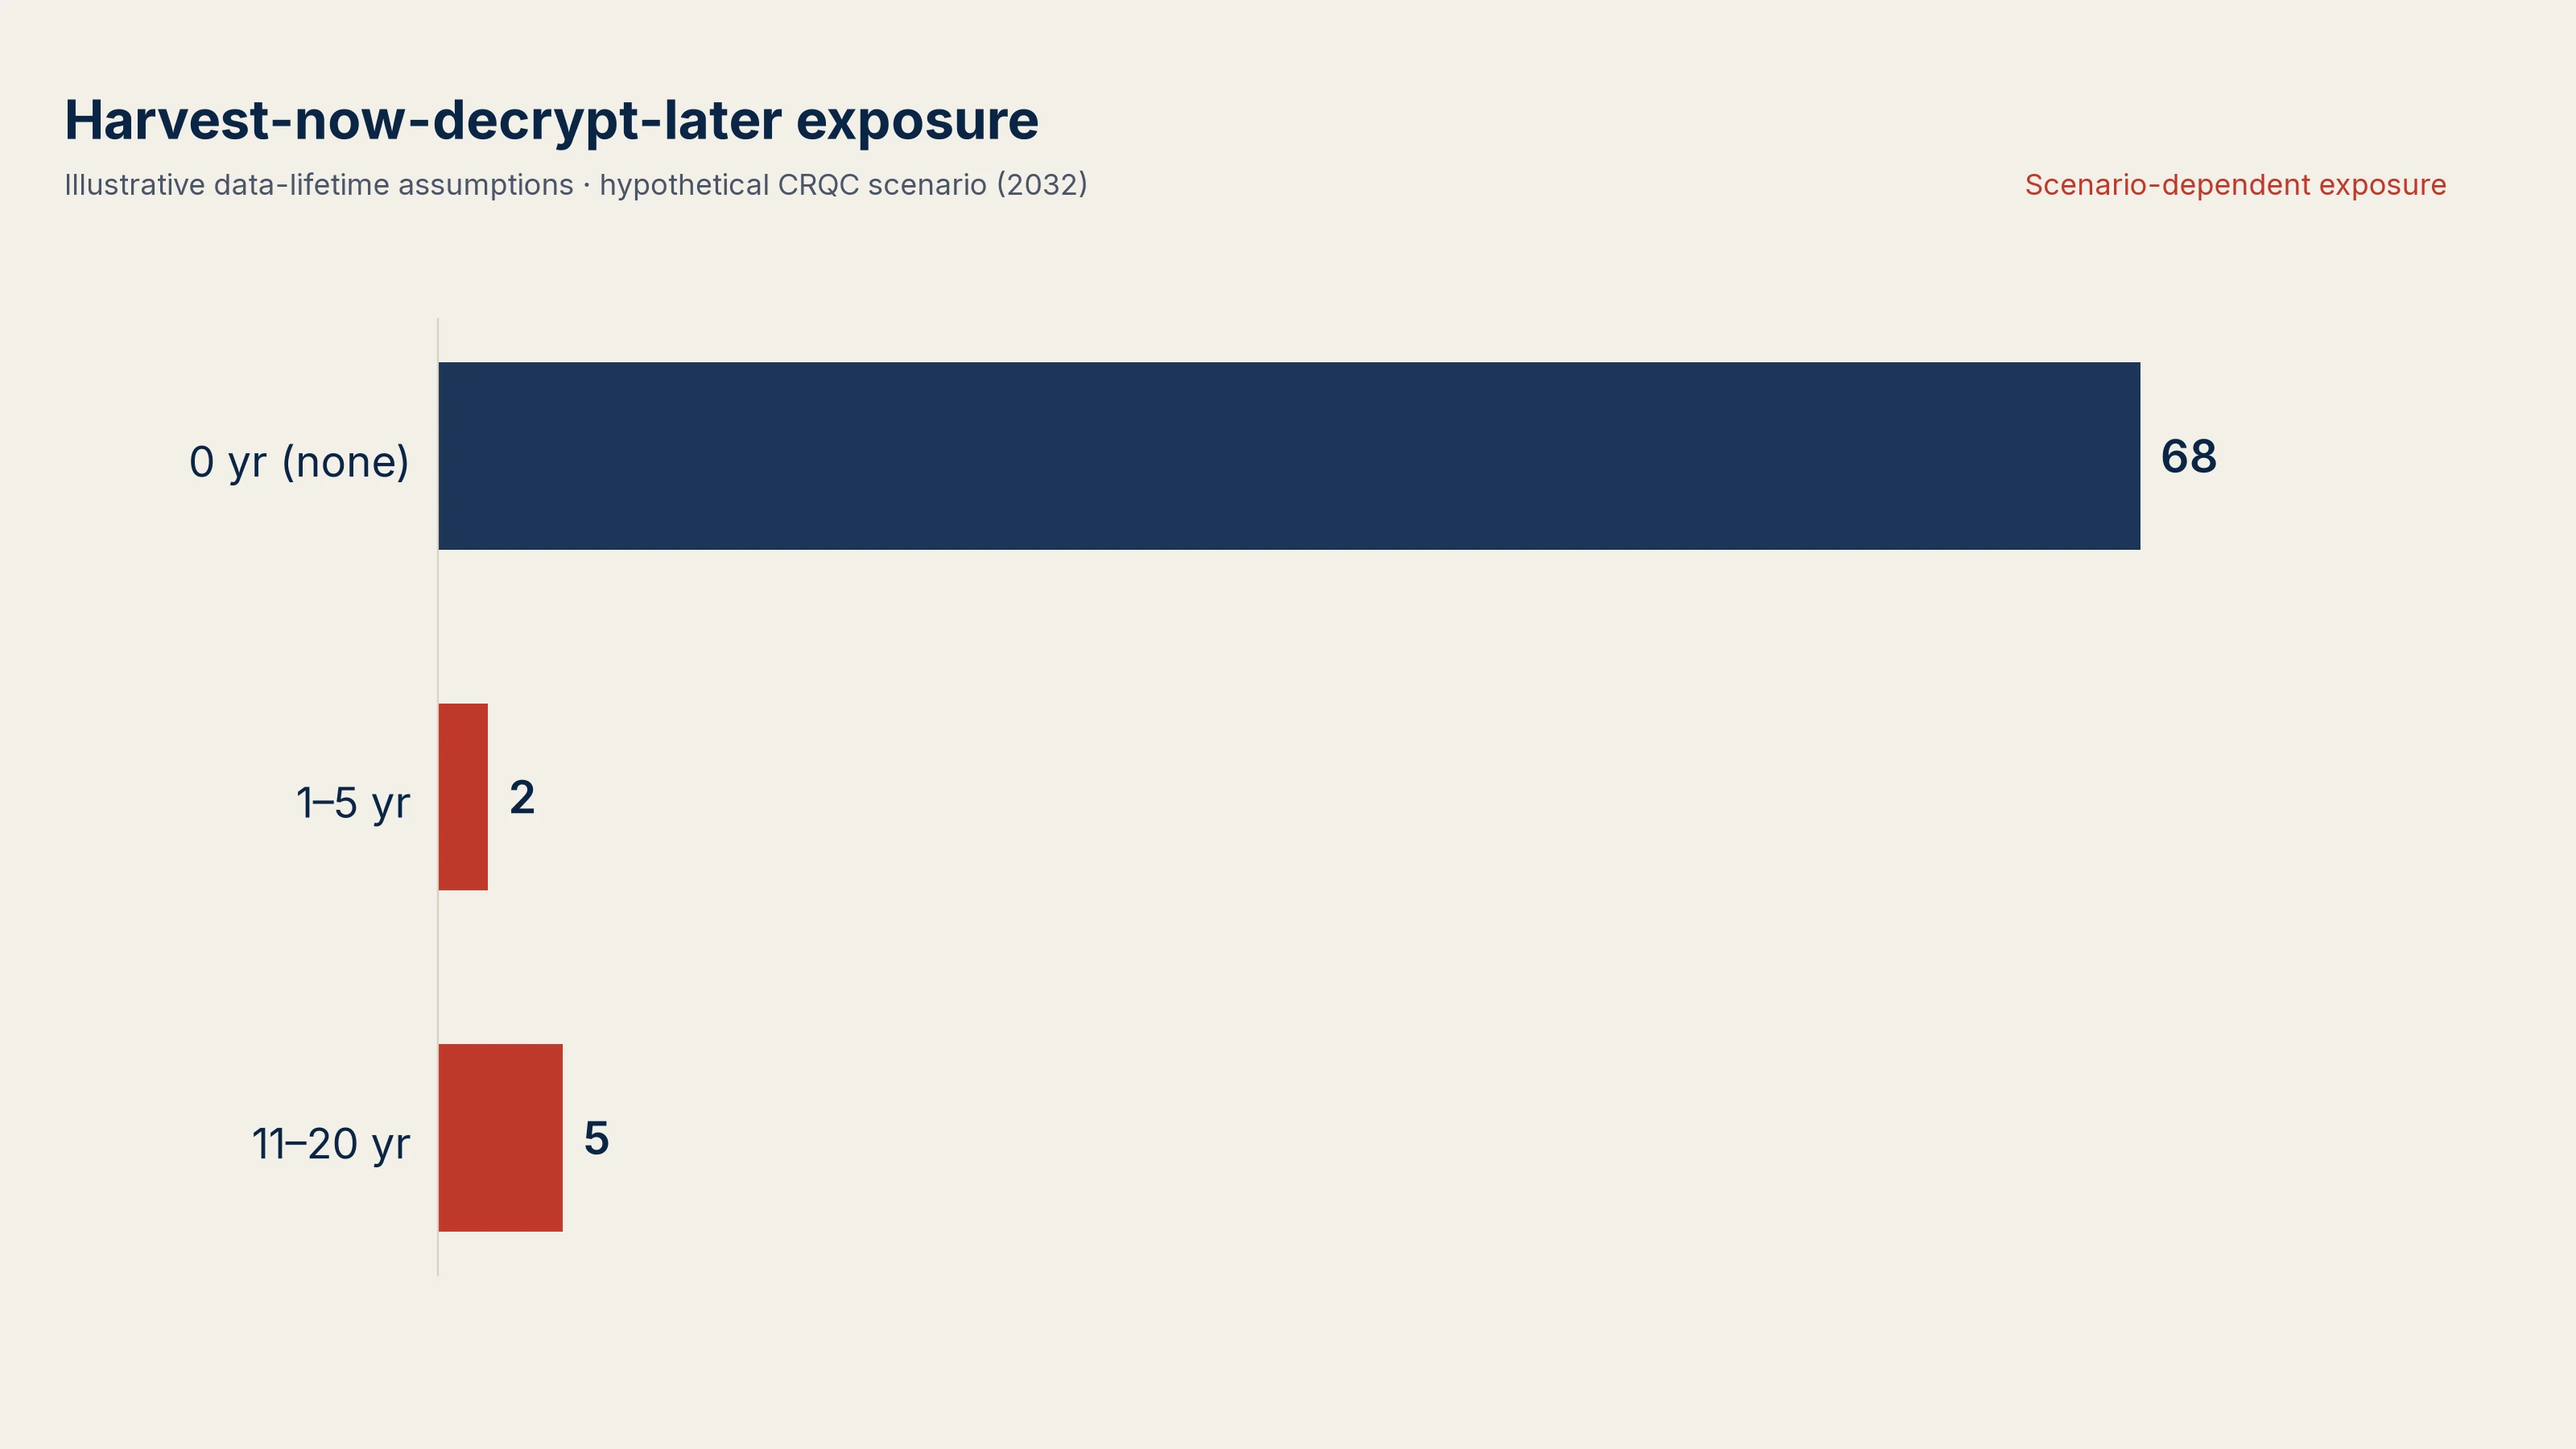
Data that must stay confidential beyond roughly seven years is already inside the harvest-now-decrypt-later window under a 2032 CRQC planning scenario. That is a planning assumption, not a prediction. How HNDL is scored →
CRYPTAGION discovers, inventories and governs cryptography across software estates, then turns that inventory into a crypto-agility and PQC migration plan.
Static analysis across five languages, plus X.509 cert stores and live TLS endpoints.
0–100 score per asset, with reasoning. Tunable per data sensitivity and HNDL window.
.cryptagion.yamlA board-ready PDF, a standards-compliant CBOM, and a 4-wave migration roadmap — generated automatically.
CRYPTAGION separates today's cryptographic debt from future post-quantum migration candidates, and from the cryptography you should simply keep and monitor. Each finding comes with its recommended replacement.
MD5 · SHA-1 · RSA-1024 · expired certificates
Already broken or out of policy. No quantum computer needed: this is current cryptographic debt, and it goes first.
RSA · ECDSA · ECDH · DH · Ed25519
Sound today, breakable by Shor's algorithm. Sequenced into migration waves towards ML-KEM and ML-DSA by HNDL exposure and data sensitivity.
AES-256 · SHA-256+ · SHA-3 · HMAC
Quantum-resistant at current parameters. Keep it, track it in the inventory and re-check as guidance evolves.
$ cryptagion scan code --path ./platform --languages java,go
$ cryptagion risk score --top 15
$ cryptagion export cbom --output cbom.json
$ cryptagion roadmap generate -r dora,nis2,cra
$ cryptagion report pdf -o report.pdf
Source code stays where it is. The cryptographic inventory comes out.
CRYPTAGION scans code, certificates, and TLS endpoints inside your perimeter, normalizes cryptographic assets, scores quantum exposure, and generates audit-ready outputs for security, architecture, and compliance teams.

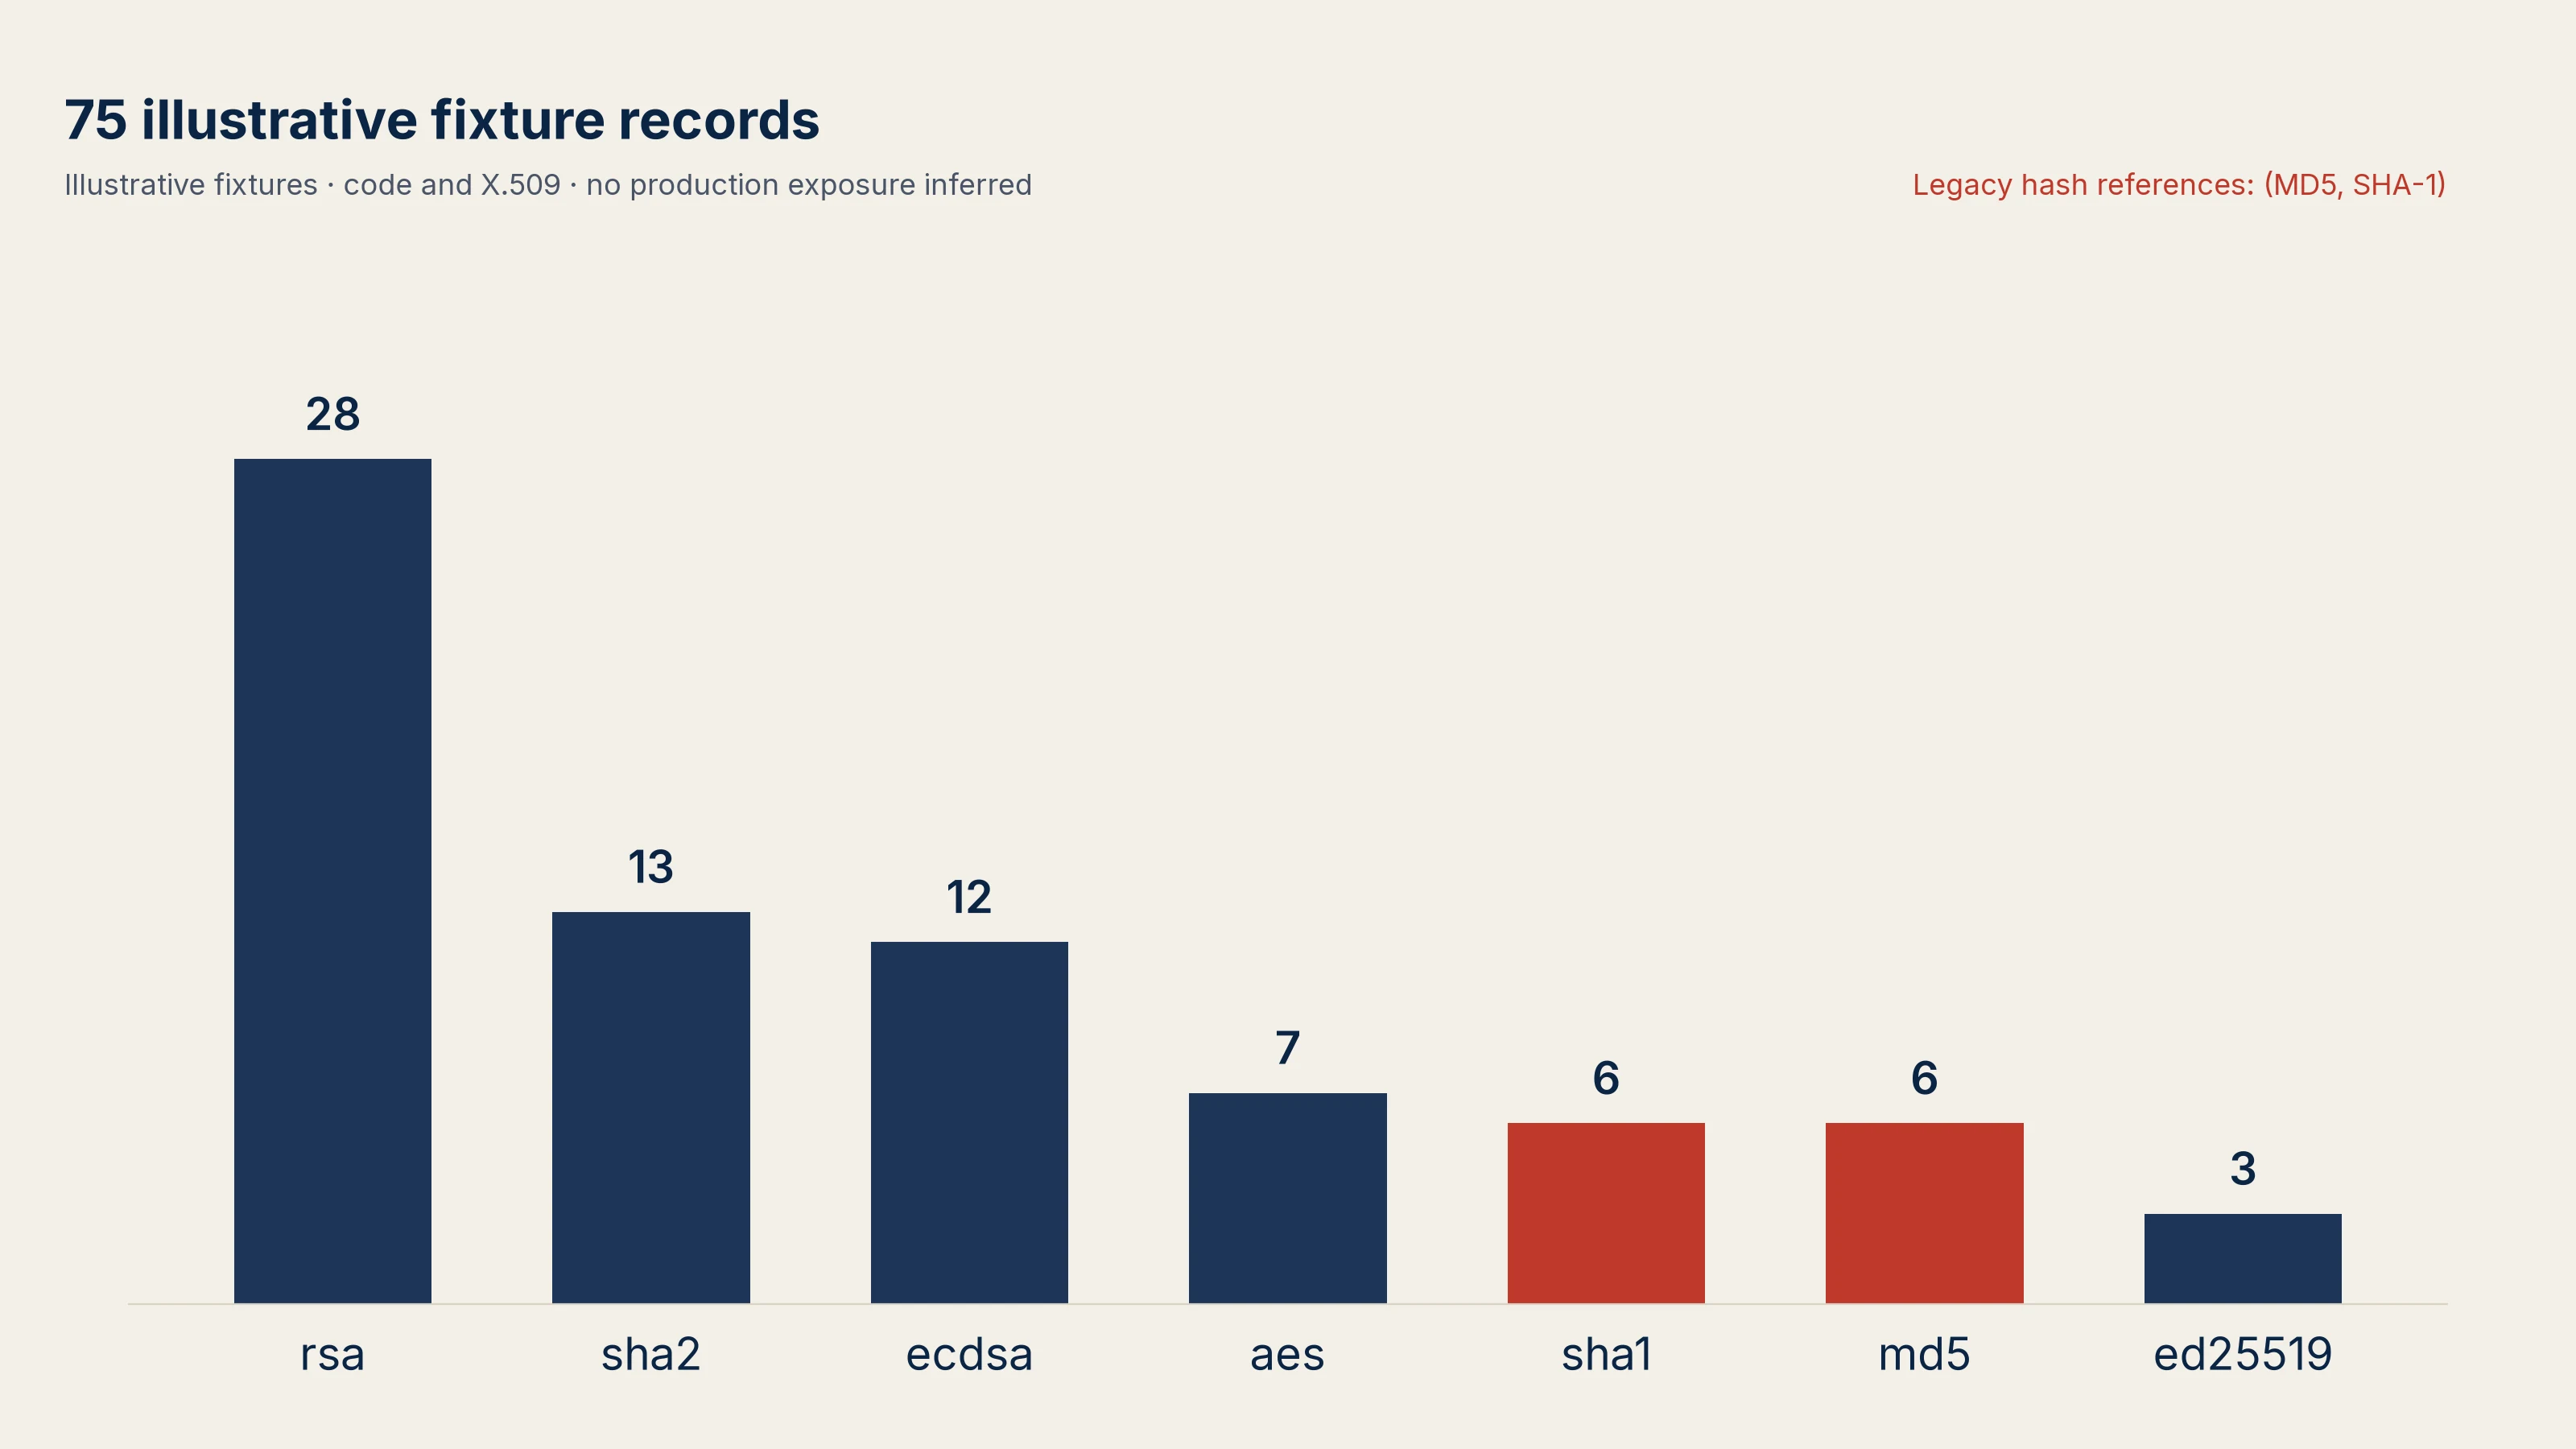
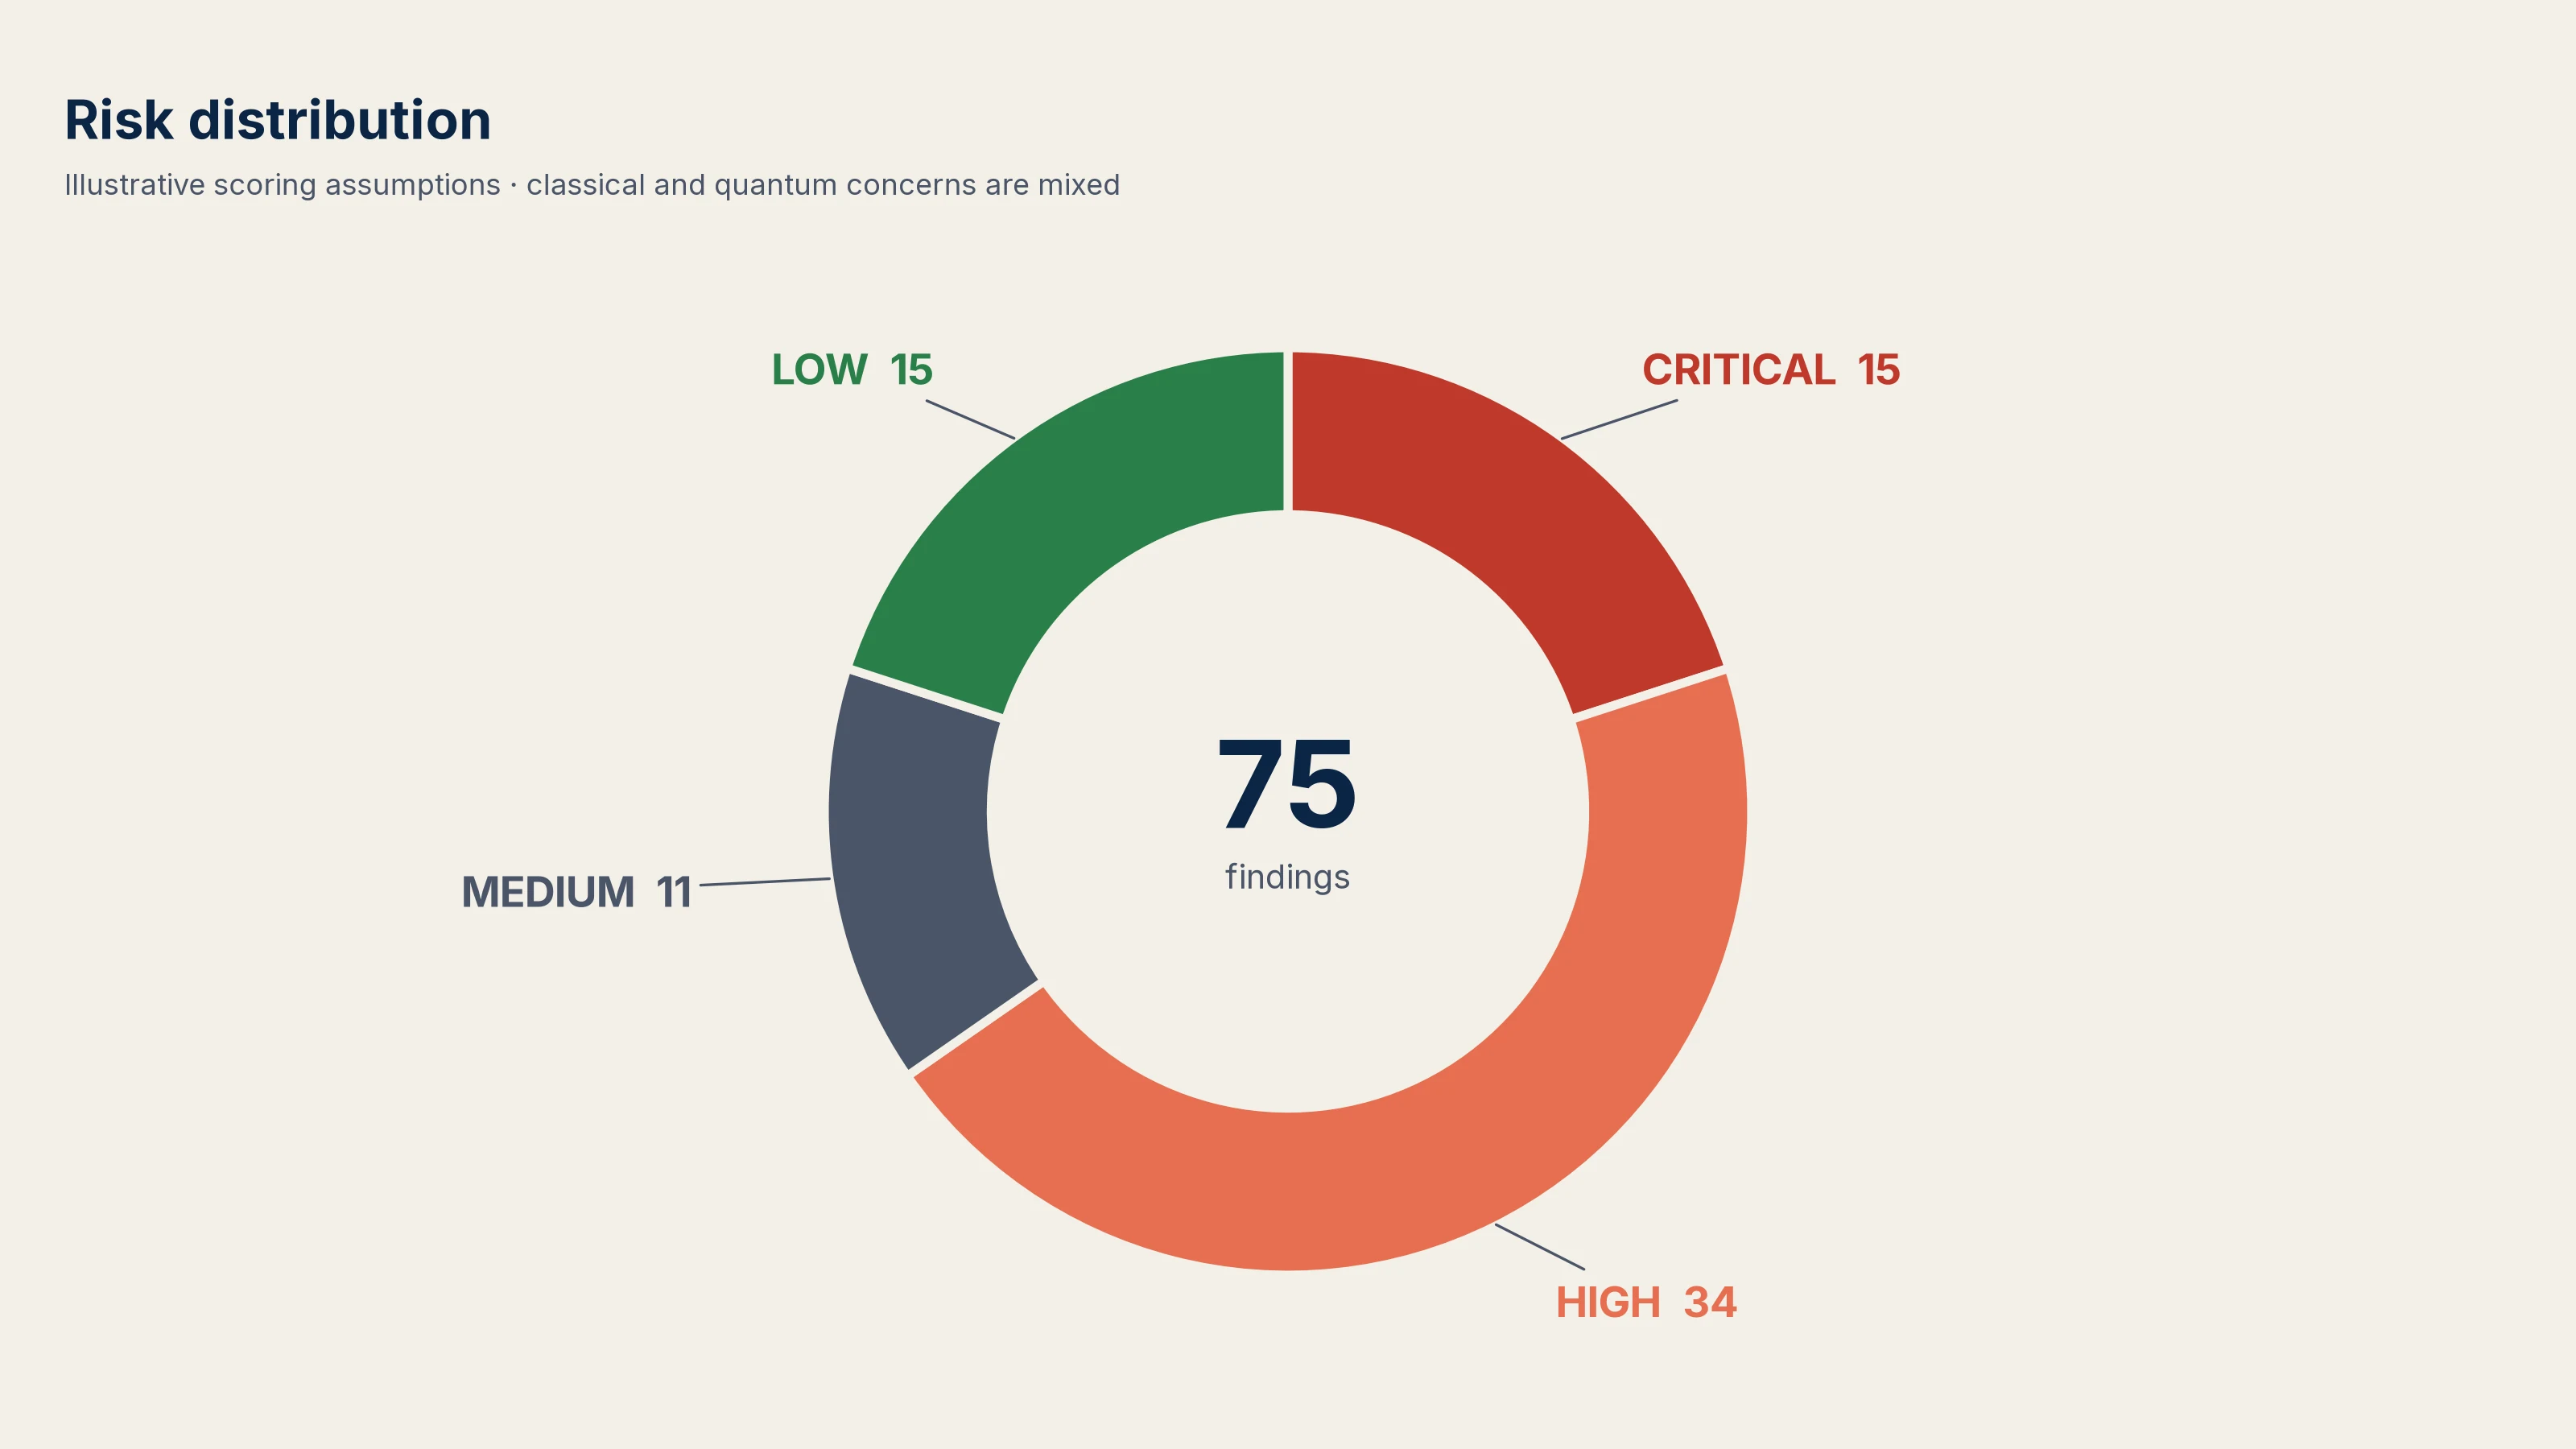
An illustrative replay using multi-language fixtures — 75 records, with assumed scoring inputs. These are not pyca/cryptography results. Click Run to play it through; to run it against your code, the first call is free.
Want to see this against your code? The first call is free. Book 30 minutes →
243 Python files scanned twice at a pinned pyca/cryptography revision. Both runs produced matching normalized findings; the CBOM passed the official CycloneDX 1.6 schema.
1,804 raw detections: 46 in library source, 1,746 in tests, 12 in documentation scripts. Detections are not vulnerabilities. Rust and Python stub files are outside this scan.
No ambiguity about what is supported today versus on the roadmap.
| Capability | Status | How |
|---|---|---|
| Python cryptography detection | Available | AST-based static analysis |
| JavaScript / TypeScript detection | Available | Static analysis (Semgrep) |
| Java detection | Available | Source-code analysis |
| Go detection | Available | Source-code analysis |
| C / C++ detection | Available | Source-code analysis |
| Certificate parsing | Available | PEM, DER, CRT, CER |
| TLS endpoint scan | Available | Live handshake inspection (sslyze) |
| Quantum risk scoring | Available | Per-asset, HNDL-aware |
| CycloneDX CBOM export | Available | Version 1.6, schema-validated |
| Executive PDF report | Available | Board & audit ready |
| CI/CD integration | Platform | API / pipeline integration |
| SOAR / GRC integration | Platform | API-driven outputs |
| Multi-cloud KMS scan | Platform | AWS KMS, Azure Key Vault, GCP KMS via API |
| SIEM export | Platform | Findings streamed to your SIEM via API |
| Container image analysis | Roadmap | Planned |
| Binary analysis | Roadmap | Planned |
Practical, sourced guides on deadlines, regulation and migration — written by the people who run the scans.
The milestones every EU organisation is now measured against — and a 90-day plan to meet the first one.
Read → NIS2 · ComplianceWhy “we use TLS” is not a cryptography policy, and how to turn an inventory into audit evidence.
Read → Checklist · CISOA printable checklist covering inventory, HNDL risk, governance, suppliers and crypto-agility.
Read →Answer 10 questions, get a readiness score and your three next steps. Two minutes, no email required.
Fixed-fee discovery, transparent platform pricing, optional migration advisory. Public so your CISO does not have to "talk to sales" to budget it.
The path: PQC Readiness Pilot (€18k) → Discovery (€45k) → Platform (from €80k/year). Integrators and consultancies: a partner licence for use across customer engagements; OEM and redistribution under a separate agreement.
For your procurement file: Download the CRYPTAGION security posture (PDF) →
You are inventorying your most sensitive cryptographic assets. You should know exactly who runs the tool, where it runs, and what happens if we disappear. Here are the answers your procurement team will ask for — before they ask.
Discovery runs inside your environment. Static analysis, cert parsing and TLS handshakes execute locally; only the findings are aggregated. The executive narrative is policy-generated; optional LLM assistance uses an EU-sovereign backend you can swap, or runs in a deterministic offline mode with no external call at all. Air-gapped runs are supported.
Every deliverable is an open standard: a CycloneDX 1.6 CBOM your GRC tooling already ingests, and a PDF your board can read without our platform. If you ever stop working with us, your inventory, your roadmap and your audit trail stay fully usable.
Source-code escrow available on Platform engagements, with a documented right-to-audit and a reversibility clause. The offline fallback means a run never depends on our availability. You are buying a deliverable and a method — not a dependency.
CRYPTAGION is built by a focused security-engineering practice — cybersecurity, data & AI specialists with 10 years across banking, luxury and industrial enterprises, where cryptographic risk and regulatory pressure are operational, not theoretical. The people who scope your engagement are the people who run the tool against your code.
No. Discovery runs inside your perimeter; only aggregated findings are produced. Air-gapped runs are supported.
CycloneDX 1.6 Crypto-BOM, validated against the strict schema, with reporting mapped to DORA, NIS2, the EU CRA and FIPS 203/204/205.
No tool does that on its own. CRYPTAGION supports evidence for cryptographic risk-management, resilience and governance activities relevant to frameworks such as NIS2, DORA and the Cyber Resilience Act. Use of the product does not by itself establish regulatory compliance.
All outputs are open standards (CycloneDX CBOM, PDF) and remain fully usable without the platform. Source-code escrow is available on Platform engagements.
CRYPTAGION is a natural complement to the firms already trusted by regulated EU enterprises. Deliver post-quantum readiness to your clients without building a cryptographic-discovery engine in-house.
Extend your managed offering with cryptographic inventory, CBOM and risk scoring — under your delivery, on the client’s perimeter.
Generate CycloneDX CBOMs and board-ready reports for your DORA, NIS2 and CRA engagements — open-standard, defensible artefacts.
Pair discovery with wave-based migration roadmaps. Migration Advisory can be delivered directly or co-delivered with you.
Partner licence for multi-customer use, plus referral and co-delivery arrangements. See the partner programme →
Bring a representative repository (public, anonymised, or under NDA). You walk out with a real preview of your cryptographic posture. No payment until you've seen the tool work against your own codebase. No slides. No salesforce.
Book a free 30-minute call on CalendlyOr write directly: contact@cryptagion.io