
Most organisations cannot say where their cryptography is. CRYPTAGION Sources re-scan code, Git, certificates, TLS, keystores and cloud KMS on a schedule, resolve what was fixed and catch what was introduced.
Your cryptographic inventory should not be a spreadsheet from six months ago.
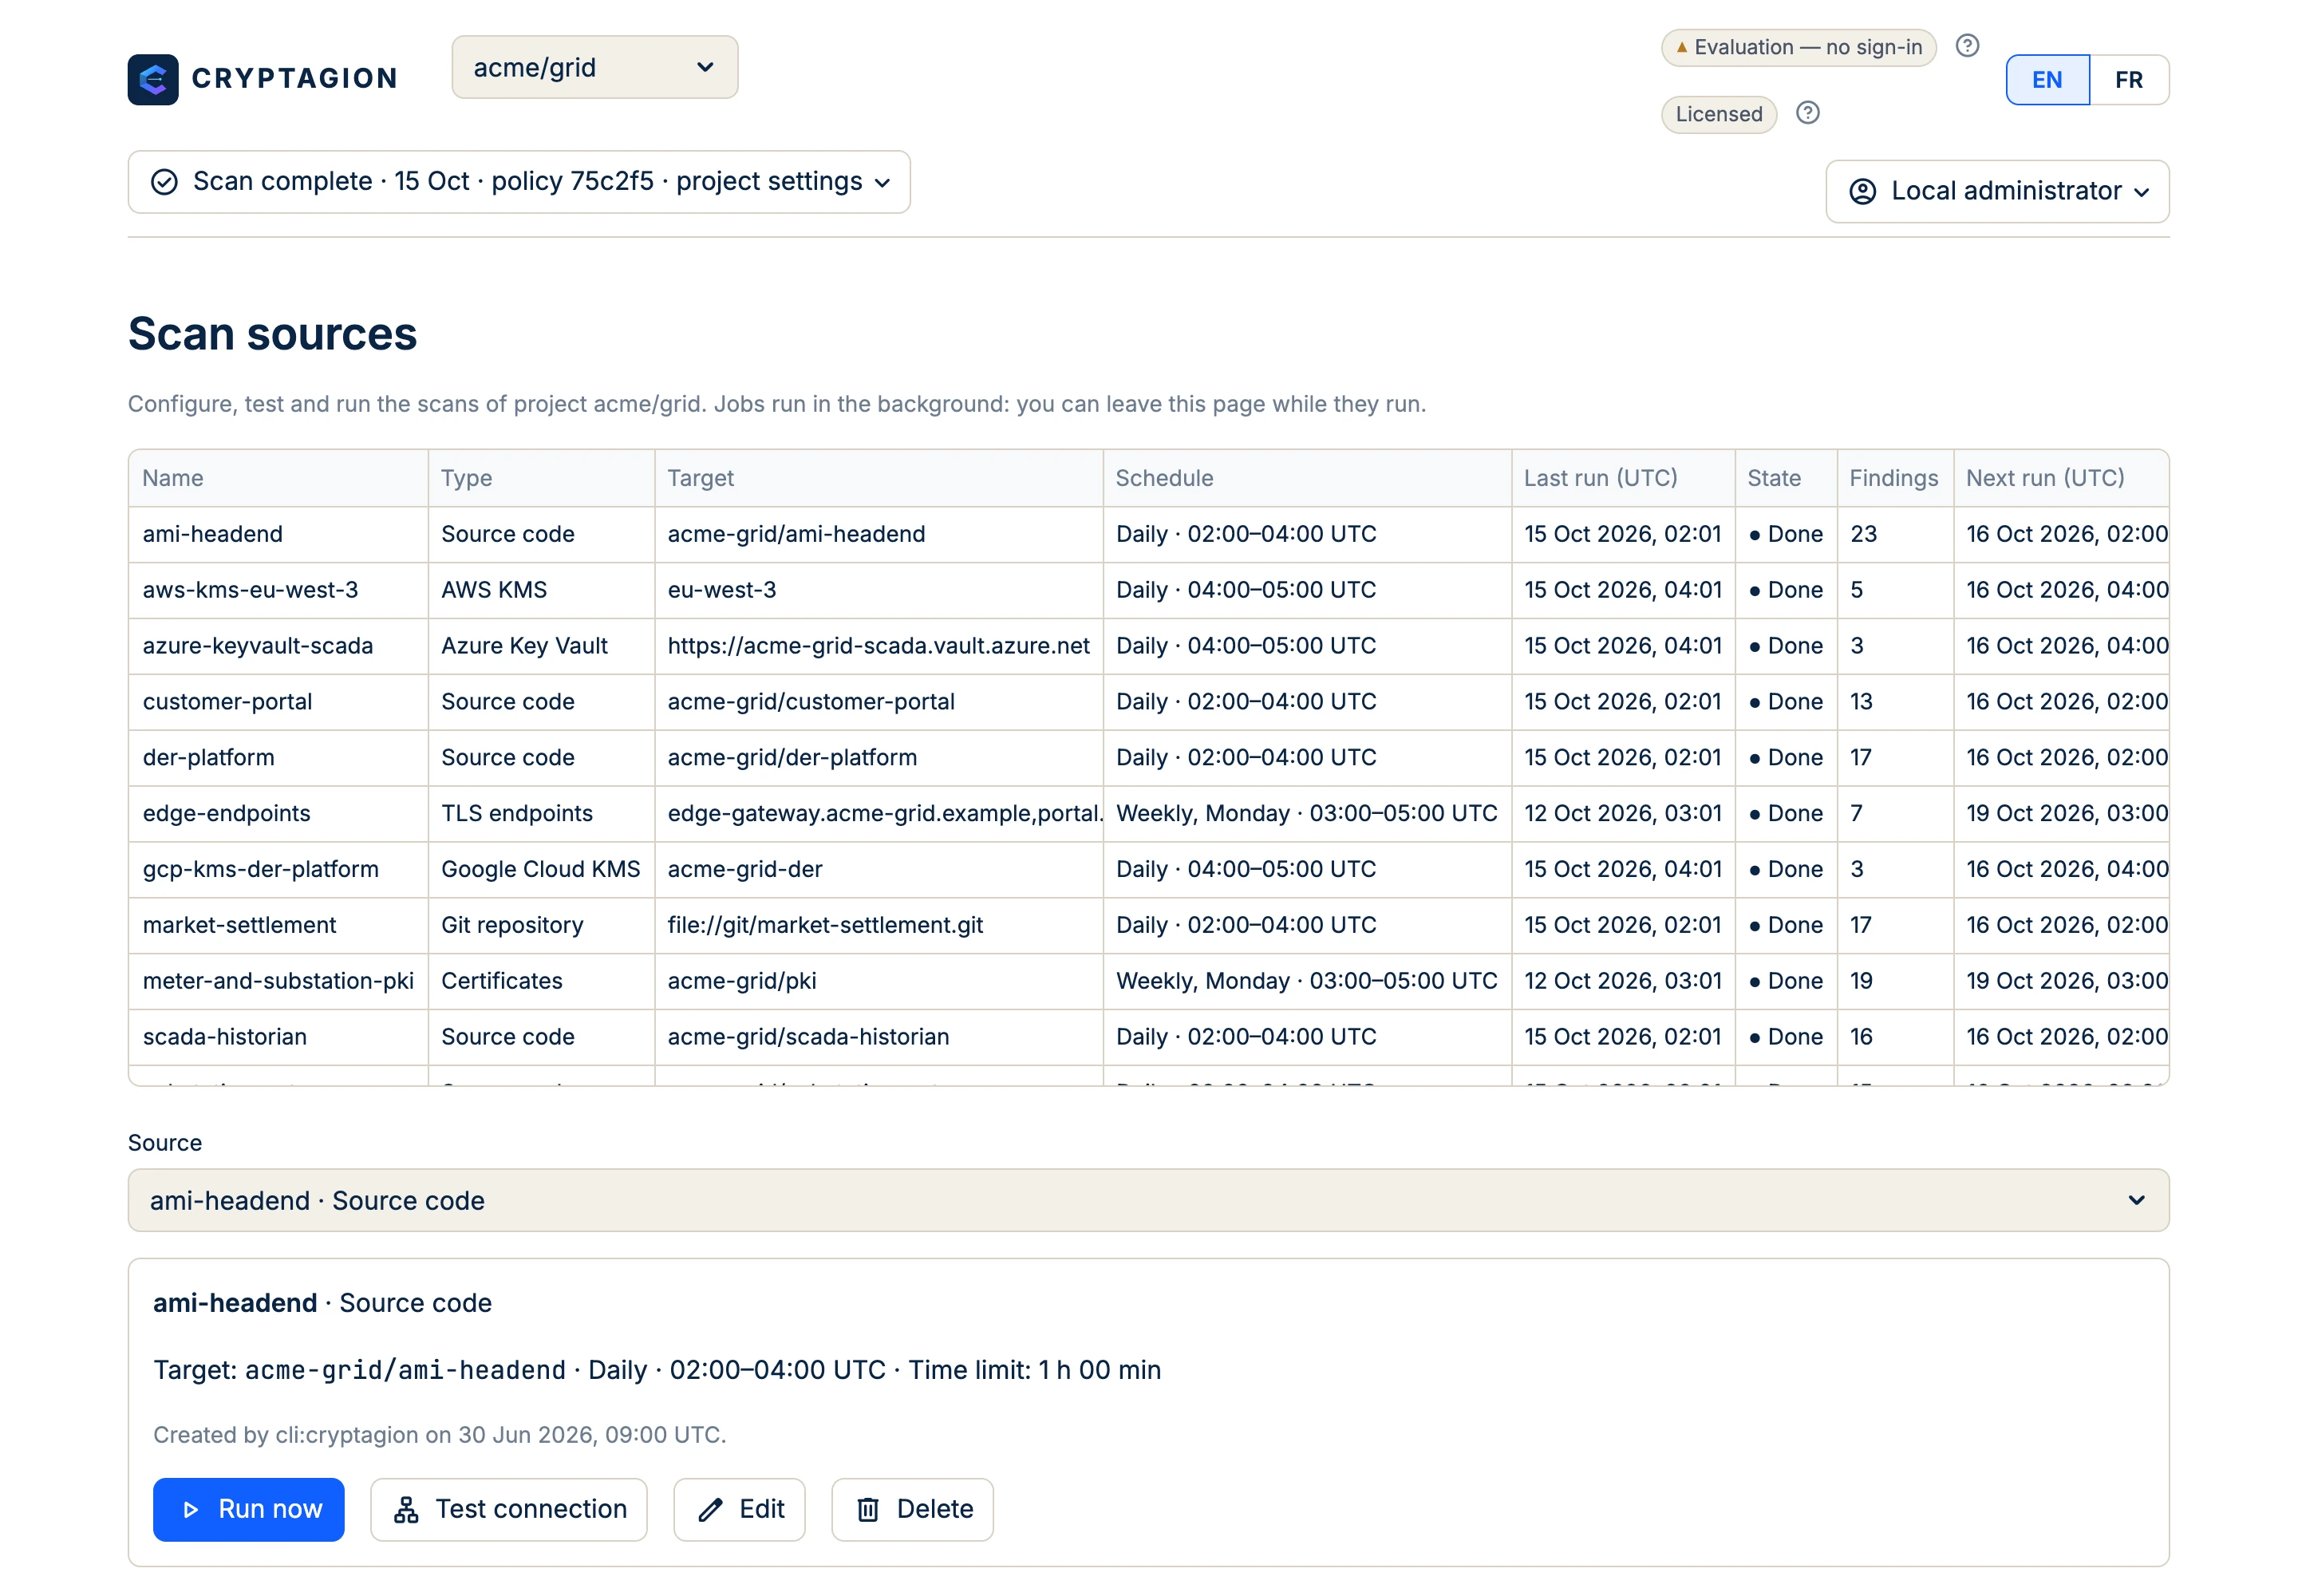
One definition per repository, folder, store, endpoint list or key vault, with its schedule and time limit.
Daily, weekly, monthly or “Run now”. Background workers run the jobs; every run keeps its log and its findings.
De-duplicated assets and findings, resolved or reopened by the next scan, ready for the CBOM.
Git, TLS, certificates, keystores and AWS, Azure or GCP key management, scanned daily, weekly, monthly or on demand by background workers.
Release 1.6.0 on a fictional demo estate. About the demo data.
What CRYPTAGION 1.6 does today, and what is still on the roadmap. Platform marks capabilities licensed with the Platform tier.
| Capability | Status | How |
|---|---|---|
| Source code | ||
| Python | Available | AST-based static analysis |
| JavaScript / TypeScript | Available | Static analysis rules |
| Java | Available | JCA and BouncyCastle source analysis |
| Go | Available | Source-code analysis |
| C / C++ | Available | Source-code analysis |
| C# / .NET | Available | Source-code analysis, including .NET Framework-only blocks |
| Git repositories | Available | Cloned at a branch or tag, HTTPS by default |
| Certificates, keys and endpoints | ||
| X.509 certificates | Available | PEM, DER, CRT, CER, with validity and signature hash |
| PKCS#12 keystores | Available | Certificates and public keys, opened in an isolated process |
| JKS / JCEKS keystores | Available | Certificates and public keys |
| TLS endpoints | Available | Live handshake inspection, including the key exchange |
| AWS KMS | AvailablePlatform | Key inventory through the provider API |
| Azure Key Vault | AvailablePlatform | Key inventory through the provider API |
| GCP KMS | AvailablePlatform | Key inventory through the provider API |
| Inventory and workflow | ||
| Scheduled discovery | Available | Daily, weekly, monthly or on demand, background workers |
| CycloneDX import | Available | Merge a CBOM produced by another tool |
| CSV import | Available | Merge an existing inventory |
| Signed remote-executor bundles | Available | Ed25519-signed results from isolated zones |
| Quantum risk scoring | Available | Per asset, HNDL-aware, sensitivity policy per system |
| Findings workflow | Available | Owners, remediation, risk acceptance, automatic resolve and reopen |
| Trend / posture history | AvailablePlatform | Snapshots, deltas, assets added and removed |
| Outputs and integrations | ||
| CycloneDX 1.6 CBOM | Available | Schema-validated export |
| CISO PDF and HTML report | Available | Board and audit ready |
| SARIF | Available | GitHub code scanning, GitLab SAST |
| CI/CD gate | AvailablePlatform | Fails a build on new weak cryptography or a posture regression |
| SIEM integration | AvailablePlatform | Splunk (HEC), Microsoft Sentinel and CEF exports, plus API access |
| Automation & GRC | AvailablePlatform | REST API, SARIF, CBOM and CSV/XLSX exports |
| Container image analysis | Roadmap | Planned |
| Binary analysis | Roadmap | Planned |
243 Python files scanned twice at a pinned pyca/cryptography revision. Both runs produced matching normalized findings; the CBOM passed the official CycloneDX 1.6 schema.
1,804 raw detections: 46 in library source, 1,746 in tests, 12 in documentation scripts. Detections are not vulnerabilities. Rust and Python stub files are outside this scan.
We run it on a public repository — one of yours, or a library your stack depends on. No access to your internal code, and you leave with a real CBOM.
We reply within one business day. · contact@cryptagion.io